

NightmareStresser Falls to the FBI
Did you know anyone could rent a massive attack against whoever they wanted?
NightmareStresser has been dismantled this week by the FBI.
For years, this service allowed anyone with no technical knowledge to launch massive DDoS attacks against targets worldwide, simply by paying with cryptocurrency.
Most alarming is that it amassed nearly one million users and could execute thousands of attacks per hour from a single platform.
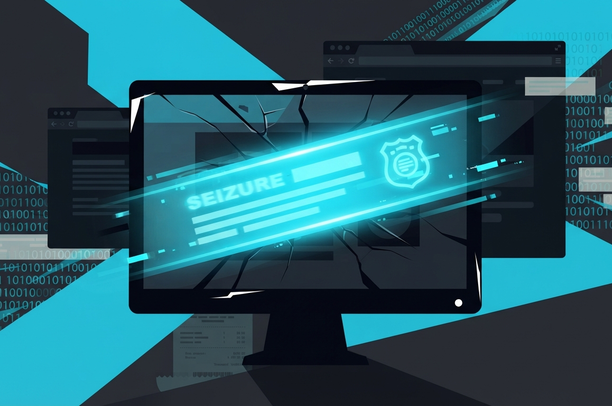
The FBI seized its official domains this very week.
The U.S. Department of Justice announced that the FBI has intervened and blocked the domains nightmare-stresser.com and nightmarestresser.org. Anyone attempting to access them now sees only an official seizure notice. Authorities confirmed that NightmareStresser had been active since at least 2022 and had been used to launch hundreds of thousands of DDoS attacks against victims worldwide.
But the real story starts much earlier.
Security researcher Alex Carter published last year that NightmareStresser likely originated in 2016. It gained popularity in 2018 when authorities dismantled rival services, and by 2019 it was already the most widely used DDoS tool in the world. It accepted cryptocurrency payments and had one notable characteristic: it deliberately avoided attacking government, university, and hospital domains.
Nearly one million users and thousands of attacks per hour.
The operation is part of the global initiative Operation PowerOFF, a coordinated effort among countries to dismantle DDoS-for-hire infrastructures and hold those who operate them accountable. This is not an isolated action: it is law enforcement’s organized response to a criminal business that has continued to grow.
NightmareStresser was not the only service of its kind.
DDoS-for-hire services, also known as booters or stressers, have multiplied because anyone without technical experience can use them to attack targets.
The barrier to entry is minimal: simply register, pay, and choose the target.
In April of this year alone, agencies from 21 countries took down 53 domains linked to DDoS-for-hire services in a single coordinated operation.
The international pressure never lets up.
Over the past eight years, the United States has charged twelve DDoS attack facilitators and seized more than one hundred domains associated with booters. Authorities are no longer just shutting down servers: they are also going after the individuals who run them.
The pattern repeats itself over and over.
Operation PowerOFF is not new. In 2024, 27 websites linked to booters were seized. Before that, the FBI dismantled the RapperBot botnet. Each operation sends a message: the DDoS-for-hire ecosystem is a priority target in the fight against digital organized crime, and law enforcement agencies from dozens of countries have been coordinating for years to strike it systematically.
Users of these services are also being investigated.
Authorities have made it clear that they are not only pursuing administrators. Those who hire attacks against third parties are also in the crosshairs. Using a booter is not anonymous: payment records can be traced, and several users have already faced criminal charges.
Paying with cryptocurrency guaranteed no one’s anonymity.
NightmareStresser accepted cryptocurrency payments, but that did not protect its users. Investigations have shown that blockchain transactions are traceable, and authorities have used that information to identify both operators and customers.
The chaos business is running out of time.
Every seized domain, every indictment, and every international operation sends a signal to the criminal marketplace: the impunity of booters is eroding. Cooperation among 21 countries in a single operation proves that the response is no longer local or slow. It is global and increasingly fast.
The net closes in on the attackers.
What appeared to be an invisible and accessible service for anyone has turned out to be a trail of evidence. And authorities know it better than anyone.
What you can do
- ✓Verify that your online services have active and up-to-date DDoS protection.
- ✓Never hire or test booters, even if they appear legal or anonymous.
- ✓Warn your team that using booters carries criminal charges.
Did you think renting an attack like this would have no consequences for you?
Security is not improvised, it is audited. At Nacata Security we detect vulnerabilities and protect your company, because a single flaw can cost you everything you have built.
Related articles
ShinyHunters Hits the FBI
Can you imagine someone stealing the personal data of FBI agents?
Moucka steals billions
Did you know someone drained one hundred and sixty-five companies from the cloud without raising any suspicion?
MonsterCloud pretended to save them
Have you ever trusted a rescuer only to discover they were part of the problem?
Talos opens its secret files
Have you ever wondered what really happens when an attack hits?

eMAPT Conquers Mobile
eMAPT, the INE certification that validates professional penetration testing on Android and iOS mobile applications.
Nacata Security, reach out to us anytime
We are Nacata Security, get to know us
web: nacata.io
email: info@nacata.io
Phone: 919930793
LinkedIn: Nacata Security
Cyberattacks that have already happened and are confirmed: hacked companies, leaked data, services down after an attack, ransoms paid.
Real cases, with names and clear consequences, explained simply so anyone understands what happened and who it affected.
RATING
9.2
Who are we?
At Nacata Security we are an offensive cybersecurity company specialized in audits and penetration testing.
We detect, assess and help mitigate the vulnerabilities of your systems, networks and applications before a real attacker exploits them, offering 360º defense tailored to each client.
We’d be glad to get in touch with you for whatever you need.