
ShinyHunters Breaches PeopleSoft Again
Does your organization manage payroll, finance, or human resources with Oracle PeopleSoft?
There is an active mass exploitation campaign targeting those systems right now.
Mandiant and Google have warned that the exploit was modified to bypass the WAF protections that many organizations believed were active and sufficient.
What appeared to be a contained threat to the education sector has spread to healthcare, government, agriculture, transportation, and technology. The perimeter expands every day.
The patch existed, but the attack mutated to bypass it.
It all started with the zero-day CVE-2026-35273, which allowed remote code execution without authentication on Oracle PeopleSoft. Attackers compromised more than one hundred organizations in June. They have now modified their exploit to bypass the WAF rules blocking the vulnerable PSEMHUB endpoint, using URL encoding of the character ‘P’ as ‘%50’ in the request path.
The firewall believed it was protecting. It was not.
The issue is technically subtle but devastating: many WAF rules compare the path before decoding it, while the PeopleSoft server decodes it before routing the request. This leaves a gap through which attackers slip their requests and reach the vulnerable servlet, even when the security team is convinced the problem is under control.
Dozens of systems already have web shells installed without anyone knowing.
Once inside, attackers deploy JSP web shells, the SideEye backdoor to steal credentials from browsers and applications, and lateral movement tools such as Neo-reGeorg and MeshCentral. They execute commands with root or System privileges and access application data, configuration files, and database connection strings.
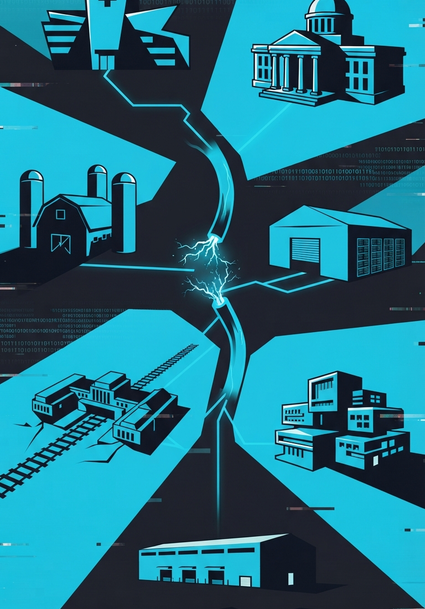
This is not a single-sector problem.
The campaign has jumped from universities to government agencies, hospitals, agricultural companies, IT providers, and transportation companies across multiple countries.
The modified exploit works against any unpatched installation that relies solely on its WAF.
In June, more than one hundred PeopleSoft customers were compromised; confirmed victims include the University of Nottingham, the NAIC, and Nissan.
The ultimate goal is extortion.
Google warns that UNC6240 has an established pattern: it steals data and threatens to publish it on a leak site if the victim does not pay. Affected organizations should prepare to receive extortion communications and monitor whether their data appears publicly exposed.
The attack on the FBI opens another dimension.
In a recent attack targeting the FBI, ShinyHunters claimed to have used a PeopleSoft zero-day. Mandiant and Google researchers believe it could be the same modified exploit, not a new vulnerability. This means the true scope of CVE-2026-35273 could be greater than expected, and that organizations that assumed they had mitigated the risk with their WAF may be exposed without knowing it.
The SideEye backdoor goes far beyond password theft.
SideEye allows attackers to manage files and processes, obtain a reverse shell, and configure a reverse proxy within the compromised network. Combined with MeshCentral as a remote management platform and Neo-reGeorg for lateral movement, attackers build a persistent presence that is difficult to detect from within.
Oracle already has the patch available: applying it is urgent.
Organizations running PeopleSoft must apply Oracle’s patch for CVE-2026-35273 immediately, review their environments for indicators of compromise, and not assume that their current WAF is sufficient to stop this modified exploit.
Patching is not optional if you use PeopleSoft.
Google and Mandiant also recommend actively searching for signs of data theft and preparing a response protocol for potential extortion communications. PeopleSoft and WebLogic service accounts must be audited to detect anomalous access to application data, configuration files, and database connection strings.
The window to act is closing fast.
Every day without patching is a day attackers can install a web shell and begin exfiltrating your organization’s data without anyone noticing.
What to Do Now
- ✓Apply Oracle’s patch for CVE-2026-35273 across all your environments.
- ✓Audit your WAF rules and look for indicators of compromise in your logs.
- ✓Prepare a response protocol for potential extortion communications.
Does your organization use PeopleSoft and have you already verified that the patch has been applied?
Security is not improvised, it is audited. At Nacata Security we detect vulnerabilities and protect your company, because a single flaw can cost you everything you have built.
Related articles
LiteLLM infected 2,500 companies
Did you know that a single unrevoked token can compromise thousands of organizations at once?
Passwork tames NIS2 chaos
Does your organization know exactly who is accessing which credential right now?
BitLocker Takes Companies Hostage
Can you imagine arriving at work and being unable to open a single company file?
Hunt.io Exposes BraZetsu in the Open
Did you know an access broker can move for months before anyone discovers it?

eMAPT Conquers Mobile
eMAPT, the INE certification that validates professional penetration testing on Android and iOS mobile applications.
Nacata Security, reach out to us anytime
We are Nacata Security, get to know us
web: nacata.io
email: info@nacata.io
Phone: 919930793
LinkedIn: Nacata Security
Risks and attacks happening right now: vulnerabilities being actively exploited, official alerts from cybersecurity agencies, ongoing phishing or malware campaigns.
Information meant to help you act and protect yourself before the problem reaches you.
RATING
9.1
Who are we?
At Nacata Security we are an offensive cybersecurity company specialized in audits and penetration testing.
We detect, assess and help mitigate the vulnerabilities of your systems, networks and applications before a real attacker exploits them, offering 360º defense tailored to each client.
We’d be glad to get in touch with you for whatever you need.